Hello, I'm

LEONARDSOTA.

Microsoft 365 & Cybersecurity Engineer

I secure, audit and automate Microsoft 365 environments. From support to security, I turn field needs into tools that run in production.

Paris area · FR / EN / IT

Leonard Sota
SC-200Microsoft certified
5+years on Microsoft
3Microsoft certifications
17detailed projects
1software sold
Scroll
00 / Manifesto

I read Microsoft 365 logs, alerts and configurations like an attacker, I measure read-only, I prove every finding, then I fix with human approval. The result: tools that run in production, not slides.

01 / Selected work

Tools that run.

01 / 06Keep scrolling, the projects slide byAll projects
01Commercial product

AuditM365

Microsoft 365 & Intune security audit

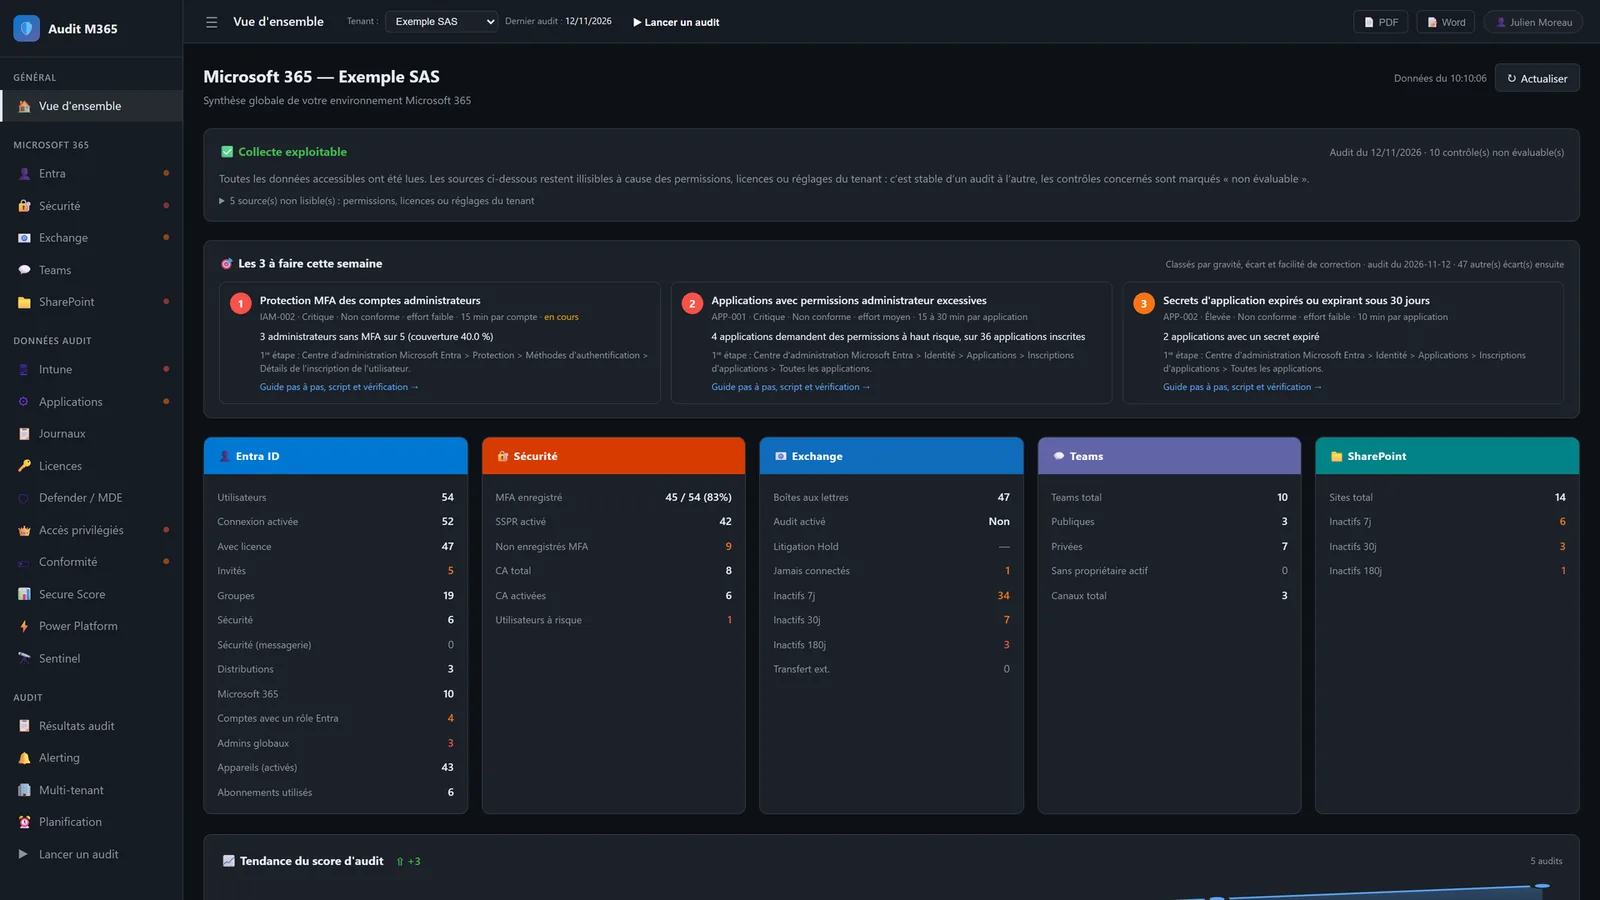
Software I design, build and sell on my own: it audits a full Microsoft 365 tenant read-only and produces a client-ready report mapped to CIS, ISO 27001, NIS2, ANSSI and GDPR.

86security controls
17Microsoft 365 domains
5frameworks
See project
02Internal tool in production

Vigil

Microsoft 365 security investigation & audit agent

An augmented SOC analyst: it reads Defender XDR, Entra ID, Exchange, Intune, Purview and Sentinel read-only, investigates with KQL hunting and returns a full report — verdict, timeline, indicators, MITRE ATT&CK, remediation — or a three-level security audit.

33scored controls per audit
30+KQL hunting playbooks
3audit levels
See project
06Lab

Defensive lab

network intrusion detection (IDS)

A Suricata IDS on my Internet-facing server: 53,500 ET Open rules, alerts in EveBox, SSH bots banned, and a commented report produced by a read-only AI agent.

53,500active ET Open rules
0.24%packet loss
1 hfail2ban ban, escalating
See project
The tools behind the work
PowerShellPythonKQLNode.jsC#Microsoft GraphDefender XDRSentinelOpenSearchDockerClaude
03 / Approach

Engineering precision. security instinct.

“
I measure.I prove.Then I fix.
LeonardMy rule, from audit to incident

From measurement to remediation

  1. 01
    Measure

    Read the tenant read-only, on complete lists, no sampling.

  2. 02
    Prove

    Every finding rests on evidence that was read, never on assumptions.

  3. 03
    Fix

    Propose the fix, have a human approve it, then apply it.

  4. 04
    Monitor

    Detections, reviews and regular audits so it holds over time.

Roles & skills

  • Microsoft 365 & Workplace EngineerIONIS Education Group
    Now
  • Founder & developerAuditM365
    Since 2026
  • Security Operations AnalystSC-200 certified
    2025
Defender XDRKQLSentinelEntra IDIntunePurviewExchangeAzurePowerShellPythonISO 27001NIS2
04 / Detection & response

An alert that tells a story.

How my tools turn Microsoft 365 logs into decisions. Click a stage.

01 / 05

Sources

Defender XDR · Entra ID · Exchange · Purview

Sign-in, unified audit, mail logs and Defender alerts from every tenant, read-only.

02 / 05

Collection

PowerShell · Graph · every 30 min

Automatic ingestion resuming where the previous cycle stopped; data isolated per customer (SecureOps 365).

03 / 05

Detection

8 rules · KQL hunting

Brute force, new global admin, MFA disabled, forwarding rule, app consent… plus Defender XDR advanced hunting.

04 / 05

Investigation

Vigil · MITRE ATT&CK

The agent reads the tenant itself: sign-ins by IP, malicious mail, inbox rules, indicator reputation, verified MITRE techniques.

05 / 05

Response

Human approval

Report with verdict and fixes; every action (revoke sessions, remove a rule) waits for the analyst's click.

05 / All projects

The toolbox.

Products, internal tools, company assignments and labs. Assignments are shown without any internal data.

01Commercial product

AuditM365

Microsoft 365 & Intune security audit

Software I design, build and sell on my own: it audits a full Microsoft 365 tenant read-only and produces a client-ready report mapped to CIS, ISO 27001, NIS2, ANSSI and GDPR.

86security controls
17Microsoft 365 domains
5frameworks

PowerShellPythonMicrosoft GraphExchange Online
02Internal tool in production

Vigil

Microsoft 365 security investigation & audit agent

An augmented SOC analyst: it reads Defender XDR, Entra ID, Exchange, Intune, Purview and Sentinel read-only, investigates with KQL hunting and returns a full report — verdict, timeline, indicators, MITRE ATT&CK, remediation — or a three-level security audit.

33scored controls per audit
30+KQL hunting playbooks
3audit levels
Node.jsPowerShellMicrosoft GraphDefender XDR
03Personal project

SecureOps 365

Microsoft 365 security monitoring platform

Microsoft 365 logs turned into detections and dashboards: compromised accounts, exfiltration, invoice fraud. Started as a lab, now a multi-customer platform with data isolation.

30 miningestion cycle
8active detections
19dashboards
OpenSearchPowerShellFastAPIPostgreSQL
04Company assignment

Multi-tenant phishing simulation portal

Microsoft Defender phishing simulations and awareness training, run for every school of a group from a single interface, with sending guardrails and strict GDPR handling.

7Defender tabs reproduced
6campaign wizard steps
€0extra licence cost
LaravelPHP 8.4Microsoft GraphDefender for Office 365
05Company assignment

Multi-tenant Microsoft 365 / Entra monitoring portal

Anomalies from several tenants in one consolidated view, with one-click remediation: licences, sessions, bulk account disabling. Built as a team.

7+anomaly types
Multitenant
1 clickper fix
LaravelMicrosoft GraphKeycloak OIDCRedis
06Personal project

Entra Posture

authentication methods audit

Measure real adoption of MFA, passwordless and phishing-resistant methods without creating an App Registration or a secret. First a local web dashboard, then a native Windows application.

0secrets to create
1 clickadmin sign-in
4axes: MFA · passwordless · phishing-resistant · SSPR
C#.NETWPFMSAL
07Lab

Defensive lab

network intrusion detection (IDS)

A Suricata IDS on my Internet-facing server: 53,500 ET Open rules, alerts in EveBox, SSH bots banned, and a commented report produced by a read-only AI agent.

53,500active ET Open rules
0.24%packet loss
1 hfail2ban ban, escalating
Suricata 8EveBoxfail2banDocker
08Lab

Offensive lab

supervised web penetration testing

A web pentest lab on a dedicated server: passive and active ZAP scans against a training target, then an AI pentest agent, all under written rules of engagement. In progress.

3ZAP scans (passive, active, AJAX)
1proven SQL injection
6non-negotiable rules
OWASP ZAPOWASP Juice ShopDockerLinux
09Personal project

SIEM for Microsoft Entra ID and Microsoft 365 (Splunk & Wazuh)

SOC search and dashboards on Entra ID logs without depending on Sentinel, plus a dozen Microsoft 365 detection sets for Wazuh.

2SIEMs
12M365 detection sets
1dedicated Entra index
SplunkWazuhAzure Event HubMicrosoft Graph
10Company assignment

SAML identity federation migration to Entra ID

Audit of a Shibboleth identity provider in the RENATER / eduGAIN federation and pilot migration plan to Microsoft Entra ID.

17federated services analysed
6 monthsof logs
1proof of concept
ShibbolethSAML 2.0Entra IDeduGAIN
11Internal tool in production

Jira Agent

AI assistant for support

Jira tickets analysed by AI with web search: diagnosis, step-by-step fix and a ready-to-post answer, with no technical account, using the agent's own SSO session.

135commits
0technical accounts
2modes: customer reply or internal note
Node.jsClaudeJira Service ManagementMicrosoft Edge
12Personal project

9 AI prospecting agents with human approval

A team of agents automating AuditM365's sales cycle: company search, qualification, writing, replies, onboarding, content and threat watch. Nothing goes out without approval.

9agents
100%of e-mails human-approved
0guessed addresses
PythonClaudeMicrosoft GraphSharePoint
13Personal project

Microsoft 365 licence management and optimisation tools

Three tools to regain control of licences: an unused-licence scanner with savings estimate, a bulk management console, and clean-up scripts for disabled accounts.

3tools
ROIestimated per licence
Simulationbefore any write
PowerShellWPFMicrosoft GraphNode.js
14Personal project

Active Directory → Entra ID provisioning console

A web portal to create and manage accounts, groups, lists and contacts directly in synced OUs, with Excel bulk processing and secure credential delivery.

6modules
Excelbulk processing
0objects created outside synced OUs
Node.jsPowerShellActive DirectoryEntra Connect
15Personal project

Keycloak SSO and role-based Ops portal

A Keycloak identity provider (local or Microsoft 365 accounts) in front of an operations portal: tool tiles with live status, admin-only n8n actions and an audit log.

2roles: user · admin
30 stool status check
0npm dependencies
KeycloakOIDCSAMLn8n
16Personal project

Multi-tenant Security Hub (MVP)

An aggregation API and a single interface for Microsoft Defender alerts and Entra ID risky users across tenants, by severity and status.

3layers: API · web · database
Multitenant
FastAPITypeScriptPostgreSQLMicrosoft Graph Security
17Personal project

Windows Update remediation tool

A PowerShell GUI that repairs Windows Update in 10 selectable steps, with built-in SetupDiag diagnostics.

10steps
1click
PowerShellWinFormsSetupDiag

Other development work

Web, mobile and desktop apps, outside security.

Pliora PDFElectron · TypeScript

PDF suite for Windows: reading, text editing, pages, signature, conversion.

MovrivaTypeScript · mobile

Adaptive fitness coaching mobile app, in production with subscriptions.

Gestion de parc de bouteilles de gazNode.js · PostgreSQL · Railway

Bilingual FR / ES web app in production for an SMB: rotation, deadlines, alerts, documents.

Gestionnaire de mots de passeFastAPI · React · MongoDB

Web vault: JWT, bcrypt, AES-256 encryption of secrets, generator.

Jarvis IATypeScript · Rust · Microsoft Graph

Local, secure Windows personal assistant: diagnostics, e-mail, calendar, no write permission.

Right now · Now building

AUDITM365.

Software I design, build and sell on my own: it audits a full Microsoft 365 tenant read-only and produces a client-ready report mapped to CIS, ISO 27001, NIS2, ANSSI and GDPR.

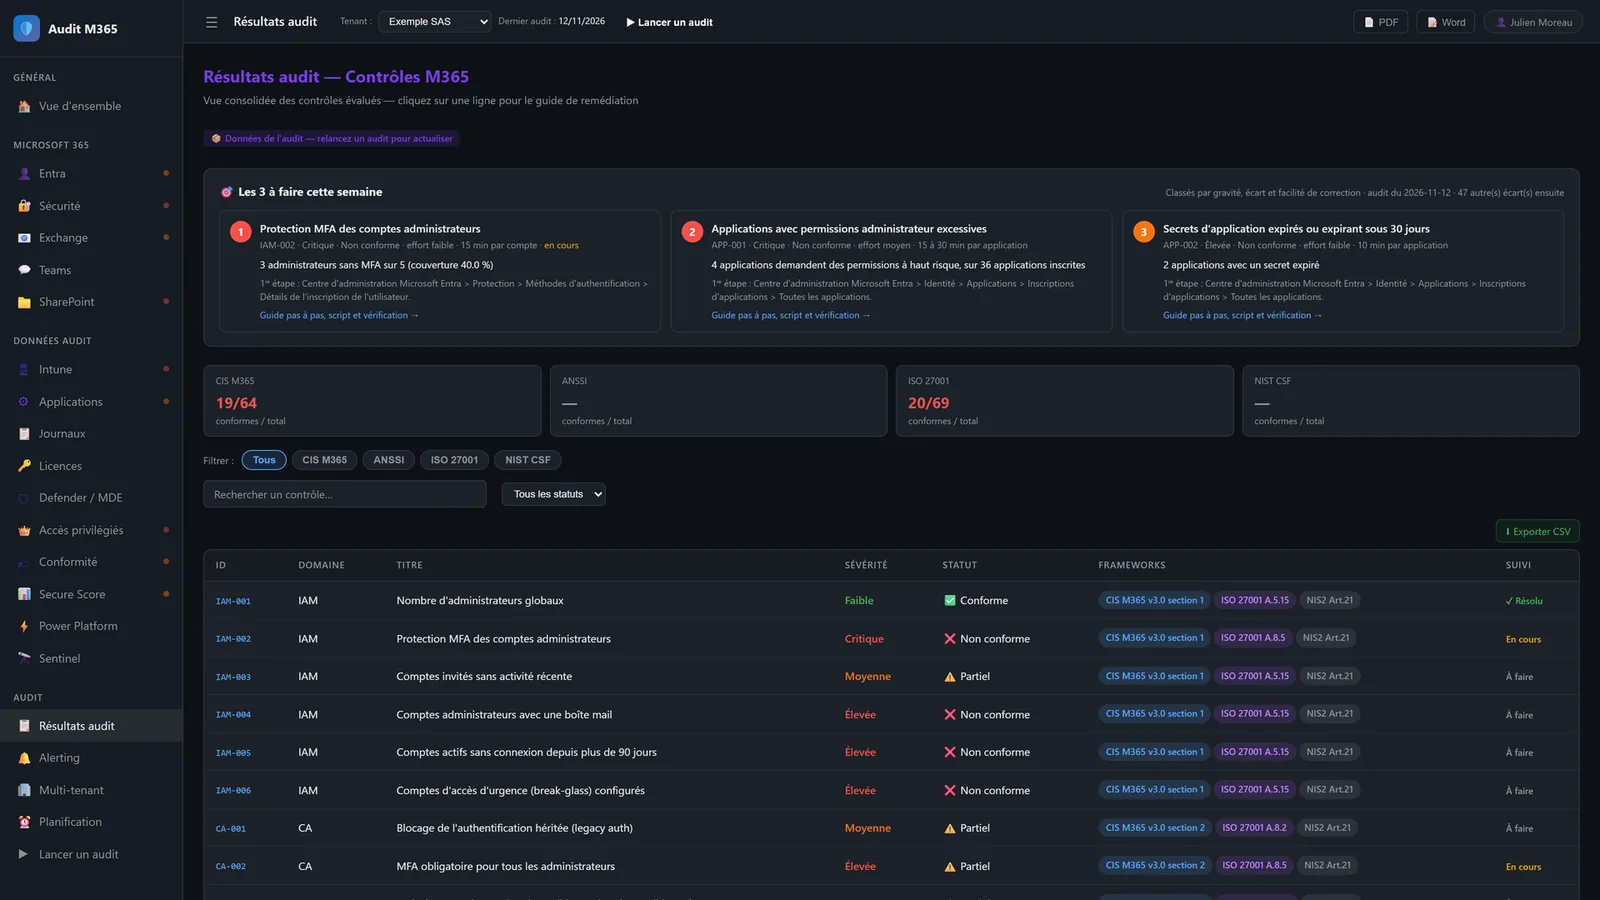
  • 86 controlsscored with evidence and remediation guide
  • 5 frameworksCIS · ISO 27001 · NIS2 · ANSSI · GDPR
  • Read-onlyno data leaves the workstation
  • ReportsPDF · Word · PowerPoint · Excel
  • MSP viewevery tenant on one screen
  • < 30 minfor a tenant with thousands of users
Audit results: 86 controls with severity, effort and remediation guide.
06 / Journey

Always progressing.

NowMicrosoft 365 & Workplace EngineerIONIS Education Group · Permanent · Le Kremlin-Bicêtre · hybrid

Apr 2026 — present

  • Microsoft Entra ID identities and Microsoft Intune endpoints across several schools and tenants.
  • Day-to-day security: Defender XDR incident investigation, privileged access reviews, reported e-mails, tenant posture.
  • Internal tooling: security investigation agent, phishing simulation portal, multi-tenant monitoring portal, AI support assistant.
  • Assessment of a SAML identity federation (Shibboleth) migration to Microsoft Entra ID.
2026 — presentFounder & developer — AuditM365Independent business · alongside

2026 — present

  • Design, development and sale of a Microsoft 365 security audit software for IT providers.
  • Full product: application, licence server, payments, public website, demo video, assisted prospecting.
Jul 2025 — Apr 2026Systems & Cloud Administrator — Windows, Exchange, M365Groupe Gagneraud · Permanent · Paris

Jul 2025 — Apr 2026

  • Administration and hardening of the Microsoft 365 tenant (Exchange Online, SharePoint, OneDrive).
  • Identity and access with Entra ID; device deployment and monitoring with Intune (compliance, updates, apps).
  • Microsoft Purview security and compliance policies: DLP, sensitivity labels, audit.
  • Operational maintenance of servers and VMware infrastructure.
  • Active Directory, DNS, GPO, WSUS and file share administration.
  • Set-up and administration of VPNs for secure remote access.
  • PowerShell automation of administrative tasks.
  • Operating procedures (Active Directory, Exchange, Intune) and application roll-outs with vendors.
  • Monitoring of systems and critical services.
Oct 2022 — Jun 2025Quanteam · Rainbow Partners GroupPermanent · 2 yrs 9 mos · Paris

Oct 2022 — Jun 2025

Application Support & Production LeadJul 2023 — Jun 2025
  • Application management and level 2/3 support, ticket tracking (Jira, ITSM), progression to team management.
  • Continuous improvement follow-up, documentation and FAQ.
Cybersecurity project — ISO/IEC 27001Sep 2023 — Oct 2024
  • Implementation of an ISMS with the cybersecurity team, towards ISO/IEC 27001 certification.
  • Policy writing (BCP, DRP, DLP…) and audit documentation.
  • Detection of malicious operations with Microsoft Defender XDR and Sentinel.
Cloud Administrator — Microsoft Azure & Microsoft 365Oct 2022 — Jun 2025
  • Azure administration (VMs, networking, storage, resource groups, NSGs, RBAC) and service continuity.
  • Data protection: DLP, Compliance Manager, sensitivity labels; Zero Trust application control with ThreatLocker.
  • Data migration to Microsoft 365; monitoring with Azure Monitor, Network Watcher and Defender for Office 365.
  • Identity and access management (Azure Active Directory), risky user analysis.
  • Microsoft 365 licence assignment and tracking.
  • Microsoft 365 tenant-to-tenant migrations with BitTitan MigrationWiz (mailboxes, OneDrive, SharePoint).
  • Azure backup and service continuity.
Mar 2022 — Oct 2022IT Support Technician — Consort NTParis · assignments for major accounts (luxury, telecoms)

Mar 2022 — Oct 2022

  • Desk-side support: device preparation and imaging, installation acceptance, daily deployment reporting.
  • Help desk: user support, Active Directory and GPO, incident tracking in ITSM, remote troubleshooting.
Jun 2021 — Jan 2022Training — IT Support TechnicianG2R Formation · Paris · qualification obtained Jan 2022

Jun 2021 — Jan 2022

  • Workstation installation and configuration; Active Directory: users, permissions, group policies, print server.
08 / Contact

Let's work together.

A role, an assignment, an audit or a technical chat?

Send a message
E-mailleonardsota@gmail.comLinkedInlinkedin.com/in/leonard-sota
LocationParis area, France
LanguagesFrench · English · Italian
AuditM365Watch the demoin 13 minutes.